Medieval ‘supership’ wrecked off the coast of Denmark discovered, largest of its kind

Archaeologists have discovered a huge medieval shipwreck at the bottom of a strait off the coast of Denmark. The 600-year-old ship was the Cogwheel, a ship with round square sails, one of the most advanced ships of the Middle Ages. Researchers at Denmark’s Viking Ship Museum say the newly discovered ship is about 28 meters […]
Three flaws in Anthropic MCP Git server allow file access and code execution
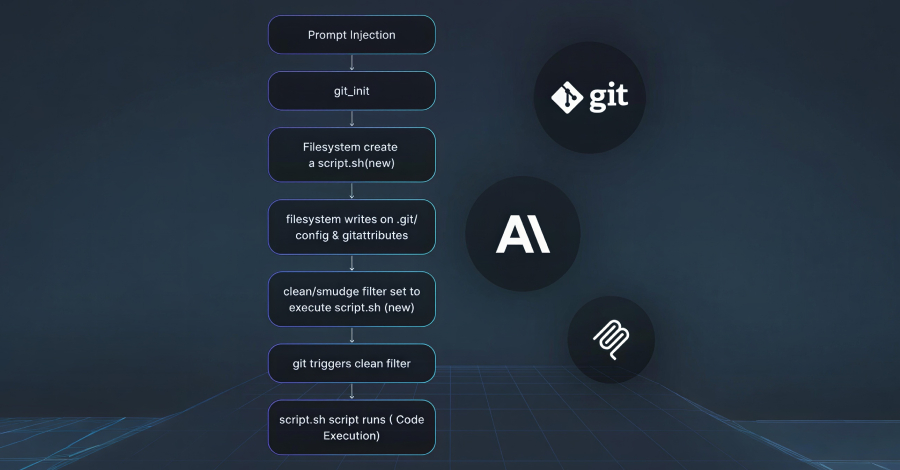
Rabi LakshmananJanuary 20, 2026Vulnerability / Artificial Intelligence A series of three security vulnerabilities have been disclosed in mcp-server-git, the official Git Model Context Protocol (MCP) server maintained by Anthropic. This can be exploited to read or delete arbitrary files and execute code under certain conditions. “These flaws can be exploited through prompt injection, meaning that […]
Indian vibecoding startup Emergent triples valuation to $300 million with $70 million funding

In a sign of the demand, or hype, for AI startups, Emergent, an Indian startup building an AI “vibecoding” platform, has raised $70 million less than four months after raising $23 million in Series A funding. The Series B round was co-led by SoftBank’s Vision Fund 2 and Khosla Ventures, valuing the startup at $300 […]
Hackers use LinkedIn messages to spread RAT malware through DLL sideloading
Ravi LakshmananJanuary 20, 2026Malware/Threat Intelligence Cybersecurity researchers have discovered a new phishing campaign that exploits private social media messages to propagate malicious payloads. This is likely intended to deploy a remote access trojan (RAT). ReliaQuest said in a report shared with The Hacker News that the activity delivers “weaponized files via dynamic link library (DLL) […]
The hidden risks of orphaned accounts
hacker newsJanuary 20, 2026Enterprise Security / AI Security The problem: residual identity As organizations grow and evolve, employees, contractors, services, and systems come and go, but often those accounts remain. These abandoned or “orphaned” accounts lie dormant across applications, platforms, assets, and cloud consoles. They persist not because of neglect but because of fragmentation. Traditional […]
Evelyn Stealer malware exploits VS Code extension to steal developer credentials and cryptography
Ravi LakshmananJanuary 20, 2026Cloud security / developer security Cybersecurity researchers have revealed details of a malware campaign that targets software developers with a new information theft tool called Evelyn Stealer, armed with the Microsoft Visual Studio Code (VS Code) extension ecosystem. “This malware is designed to exfiltrate sensitive information such as developer credentials and cryptocurrency-related […]
Cloudflare fixes ACME validation bug, allows WAF bypass to origin server
Rabi LakshmananJanuary 20, 2026Web security/vulnerabilities Cloudflare has addressed a security vulnerability that affects Automated Certificate Management Environment (ACME) validation logic and allows access to origin servers by bypassing security controls. “The vulnerability was due to the way our edge network handled requests addressed to the ACME HTTP-01 challenge path (/.well-known/acme-challenge/*),” said Hrushikesh Deshpande, Andrew Mitchell, […]
Meta Oversight Board Considers Permanent Ban in Landmark Case
Meta’s oversight board is working on a lawsuit that focuses on Meta’s ability to permanently disable user accounts. Permanent bans are drastic measures that lock out people’s profiles, memories, connections with friends, and, in the case of creators and businesses, their ability to market and communicate with fans and customers. The organization said this is […]
1,700-year-old Roman marching camp discovered in Germany – along with numerous artifacts including coins and shoe remains

German archaeologists have discovered four Roman marching camps dating back 1,700 years, along with numerous artifacts such as coins and old shoe parts. In the 3rd century AD, the Roman Empire conducted several military campaigns into what is now Germany. Their goal was to expand Roman territory northward along the Elbe River, which emptied into […]
Why the secret of JavaScript bundles is still overlooked
API key leaks are no longer uncommon, and so are subsequent breaches. So why are sensitive tokens still so easily exposed? To find out, Intruder’s research team investigated what traditional vulnerability scanners actually cover and built a new secret detection method to address gaps in existing approaches. Applying this at scale by scanning 5 million […]