Unpatched firmware flaw leaves TOTOLINK EX200 open to full remote device takeover

January 6, 2026Ravi LakshmananIoT security/vulnerabilities The CERT Coordination Center (CERT/CC) has detailed an unpatched security flaw affecting the TOTOLINK EX200 Wireless Range Extender. This flaw could allow a remote authenticated attacker to gain complete control of the device. This flaw, CVE-2025-65606 (CVSS score: N/A), is characterized as a flaw in the firmware upload error handling […]
Meta temporarily suspends overseas sales of Ray-Ban Display glasses

Meta announced Tuesday that it is suspending plans to sell Ray-Ban display glasses outside the United States, citing “unprecedented demand and limited supply.” Meta originally planned to launch the glasses in France, Italy, Canada and the UK in early 2026. “We have received overwhelming interest since our launch last fall, and as a result, the […]
Amazon’s Ring doorbell comes with fire alarm, app store, and new sensors

Amazon is enhancing the Ring smart doorbell with new features such as a new fire alarm, app store, and a new set of Ring sensors. Announced at CES 2026 in Las Vegas, the company said its new ring sensor can detect movement, openings, broken glass and smoke, as well as monitor carbon monoxide levels, leaks, […]
Fake reservation email redirects hotel staff to fake BSoD page delivering DCRat

January 6, 2026Ravi LakshmananMalware/Endpoint Security Source: Securonics Cybersecurity researchers have revealed details of a new campaign called PHALT#BLYX that leverages ClickFix-style lures to display fake Blue Screen of Death (BSoD) error fixes in attacks targeting European hospitality businesses. According to cybersecurity firm Securonix, the end goal of the multi-stage campaign is to deliver a remote […]
What is identity dark matter?
January 6, 2026hacker newsSaaS Security / Enterprise Security The invisible half of the identity universe Identity existed in one place, such as an LDAP directory, HR system, or a single IAM portal. No more. Today, identities are fragmented across SaaS, on-premises, IaaS, PaaS, homegrown, and shadow applications. Each of these environments has its own accounts, […]
VS Code forks recommend missing extensions and pose supply chain risks with Open VSX
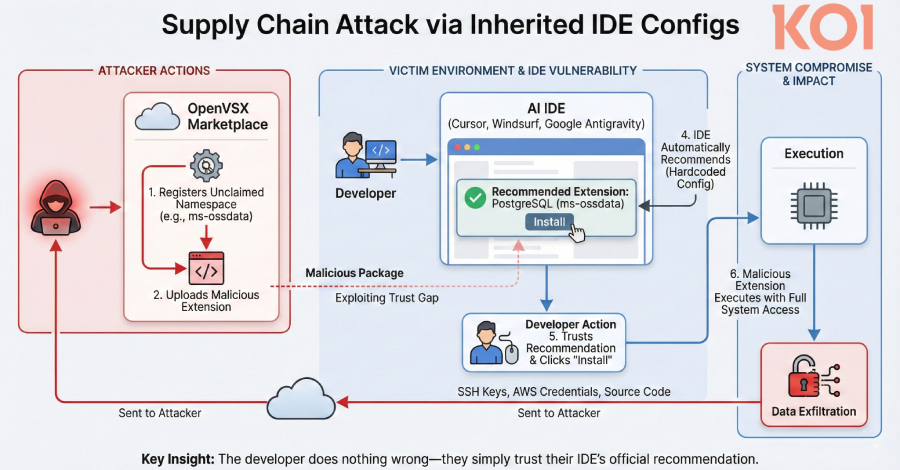
January 6, 2026Ravi LakshmananThreat Intelligence/Cloud Security Popular artificial intelligence (AI)-powered Microsoft Visual Studio Code (VS Code) forks such as Cursor, Windsurf, Google Antigravity, and Trae have been found to promote extensions that are not present in the Open VSX registry, potentially opening the door to supply chain risk if bad actors publish malicious packages with […]
1,100-year-old burial of elite warriors and their weapons discovered in Hungary – and DNA shows all three are related

Hungarian archaeologists have discovered the burials of three elite male warriors from 1,100 years ago, and DNA analysis shows they were related. The warriors’ burial goods include weapons such as sabers and bows with quivers, as well as dozens of coins. DNA analysis showed that one of the warriors may have been the father or […]
Narwal adds AI to vacuum cleaner to monitor pets and find gems

Robot vacuum cleaner maker Narwal unveiled a new smart vacuum set at the Consumer Electronics Show with AI-powered features such as monitoring pets, locating valuables, and notifying users of misplaced toys. The company said its new flagship robot vacuum cleaner, Flow 2, has a rounded design that makes it easier to lift the tank and […]
New n8n vulnerability (9.9 CVSS) allows authenticated users to execute system commands
January 6, 2026Ravi LakshmananVulnerabilities / DevOps A critical new security vulnerability has been disclosed in n8n, an open source workflow automation platform, that could allow an authenticated attacker to execute arbitrary system commands on the underlying host. This vulnerability is tracked as CVE-2025-68668 and is rated 9.9 on the CVSS scoring system. This is described […]
Critical flaw in AdonisJS Bodyparser (CVSS 9.2) allows arbitrary file writing on the server
January 6, 2026Ravi LakshmananVulnerabilities / Web Security Users of the ‘@adonisjs/bodyparser’ npm package are advised to update to the latest version following disclosure of a critical security vulnerability that, if successfully exploited, could allow a remote attacker to write arbitrary files on the server. This flaw is tracked as CVE-2026-21440 (CVSS score: 9.2) and is […]